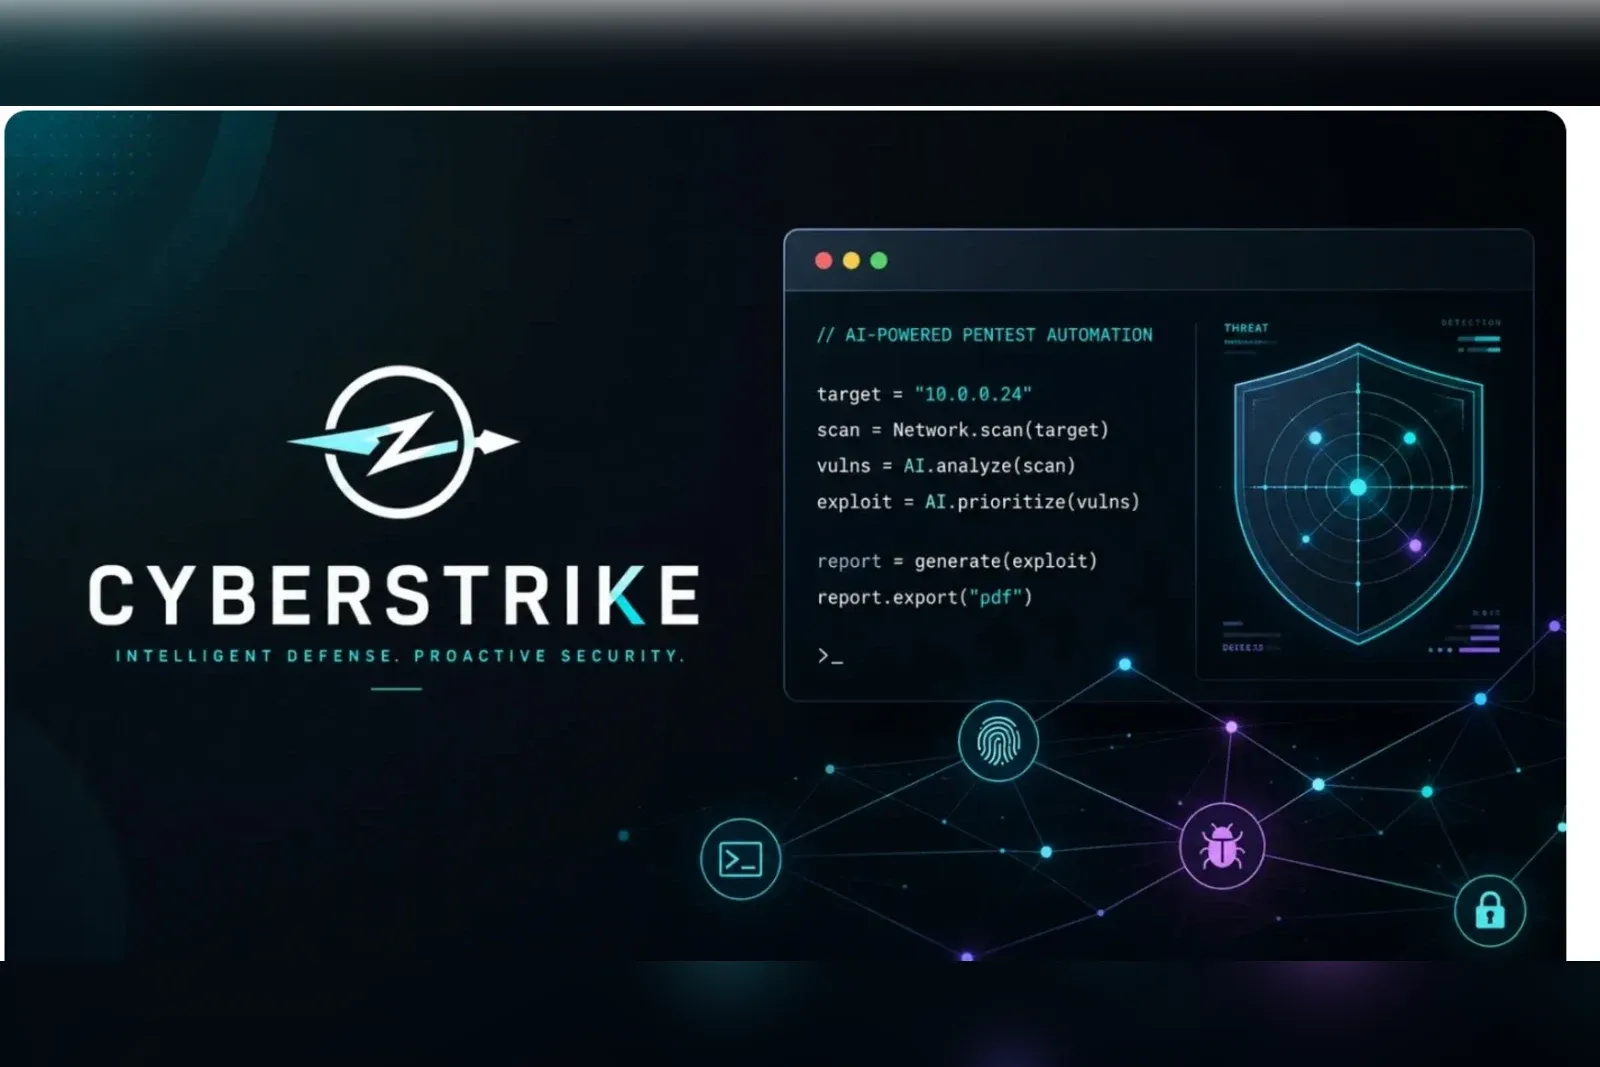
Cyber Security News published a profile of CyberStrike, framing it as an AI-powered security platform built for automated penetration testing rather than another chatbot wrapper. Here is what the piece describes, in our own words, with the source linked at the end.
What the platform does
Per the article, CyberStrike installs as a terminal-based tool that runs the full assessment loop, reconnaissance, vulnerability discovery, exploitation and reporting, without a human prompting each step. The framing is that it turns an existing LLM subscription into an autonomous red-team operator, aimed at penetration testers, bug bounty hunters and security teams trying to scale their assessments.
The intelligence layer
The article’s main point is that the useful part is not the model, it is the layer around it. CyberStrike injects OWASP testing methodology, known vulnerability patterns and attack-chain reasoning into every model interaction, so the underlying model does not need built-in security knowledge. That layer is described as schema normalization, context guarding, provider auto-detection and tool orchestration.
Models and coverage
Cyber Security News reports support for 150+ AI providers and 5,300+ models, including Anthropic, OpenAI, Google, Amazon Bedrock and Azure, plus fully offline options like Ollama and LM Studio for air-gapped environments. It also cites 13 or more domain-specific agents: web application testing on OWASP WSTG, mobile on MASTG and MASVS, cloud around CIS benchmarks, and internal network testing covering Active Directory and lateral movement.
Our read
This is press coverage, not our own benchmark, so treat the capability claims as the outlet’s. What is accurate to state from our side: CyberStrike is an AI-augmented penetration testing project, open source under AGPL-3.0, and still pre-launch. The honest version is that automation shortens the repetitive parts of an assessment; a human still owns scope, judgment and sign-off.
Related coverage
The same tooling shows up in the FortiBleed reporting, where a criminal operator misused it. For that side of the story:
- Arctic Wolf reverse-engineers the FortiBleed harvester
- The Hacker News on FortiBleed and FortiGate
- SpyCloud maps the FortiBleed infrastructure
- SoCRadar’s ‘Dismantling FortiBleed’ report
Source
- Cyber Security News, CyberStrike, AI-Powered Security Platform for Automated Penetration Testing