
Your external attack surface, continuously mapped
CyberStrike continuously discovers the domains, subdomains, IPs and services you expose across AWS, Azure, Google Cloud, Oracle and IBM Cloud, flags every new and exposed asset the moment it appears, and finds the entry points an attacker would reach first.
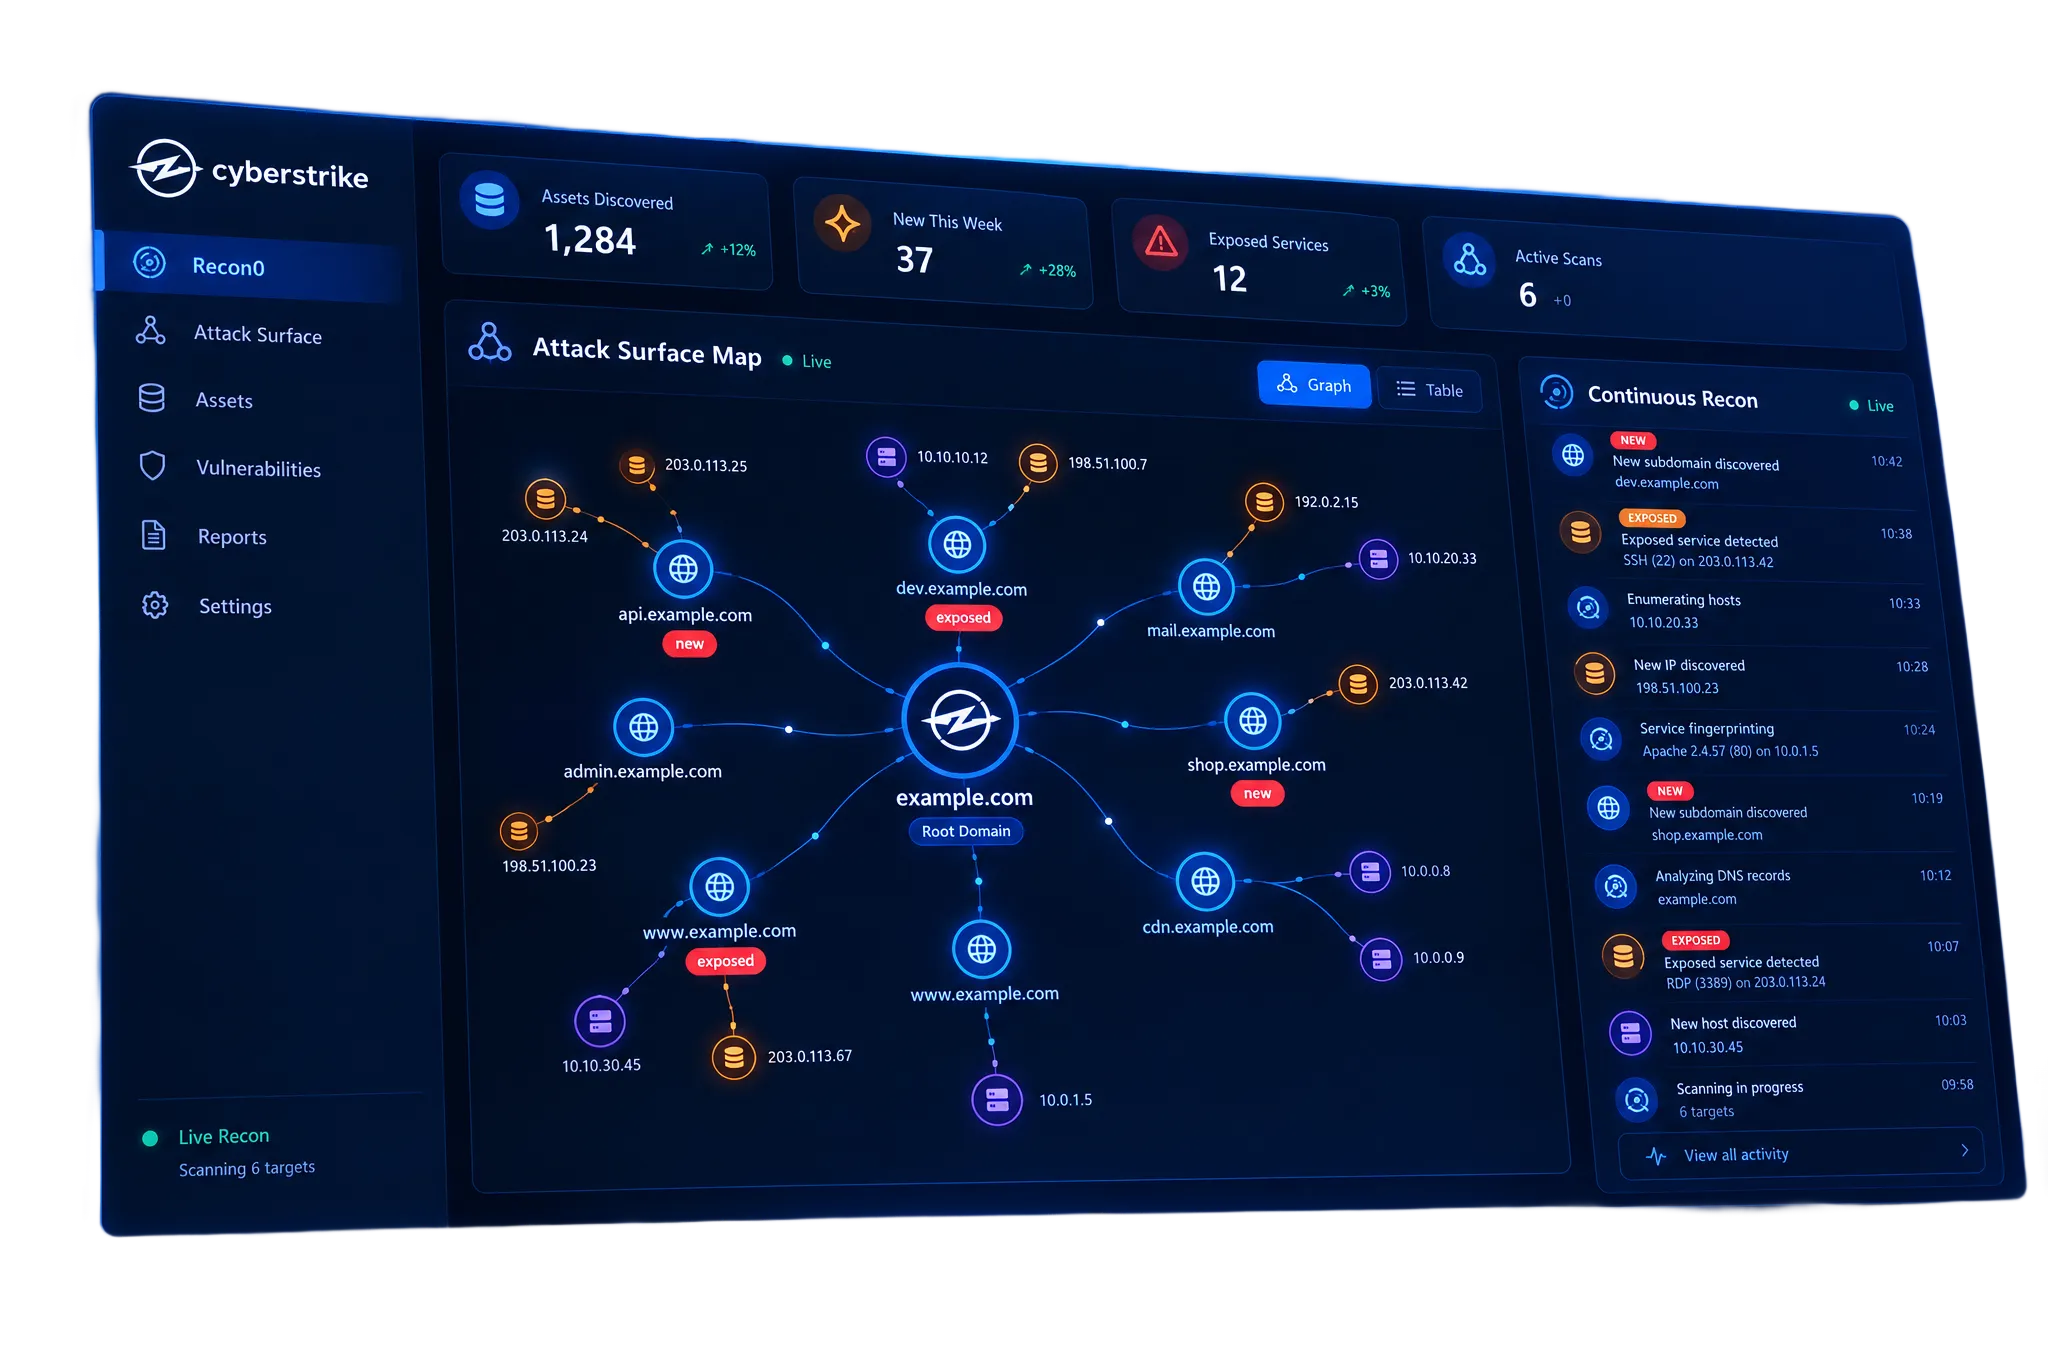
Continuous coverage across every cloud
Connect your cloud accounts and CyberStrike keeps watch as your footprint changes, mapping new assets and surfacing the exposed entry points an attacker would reach first.

Every scan makes the next one sharper
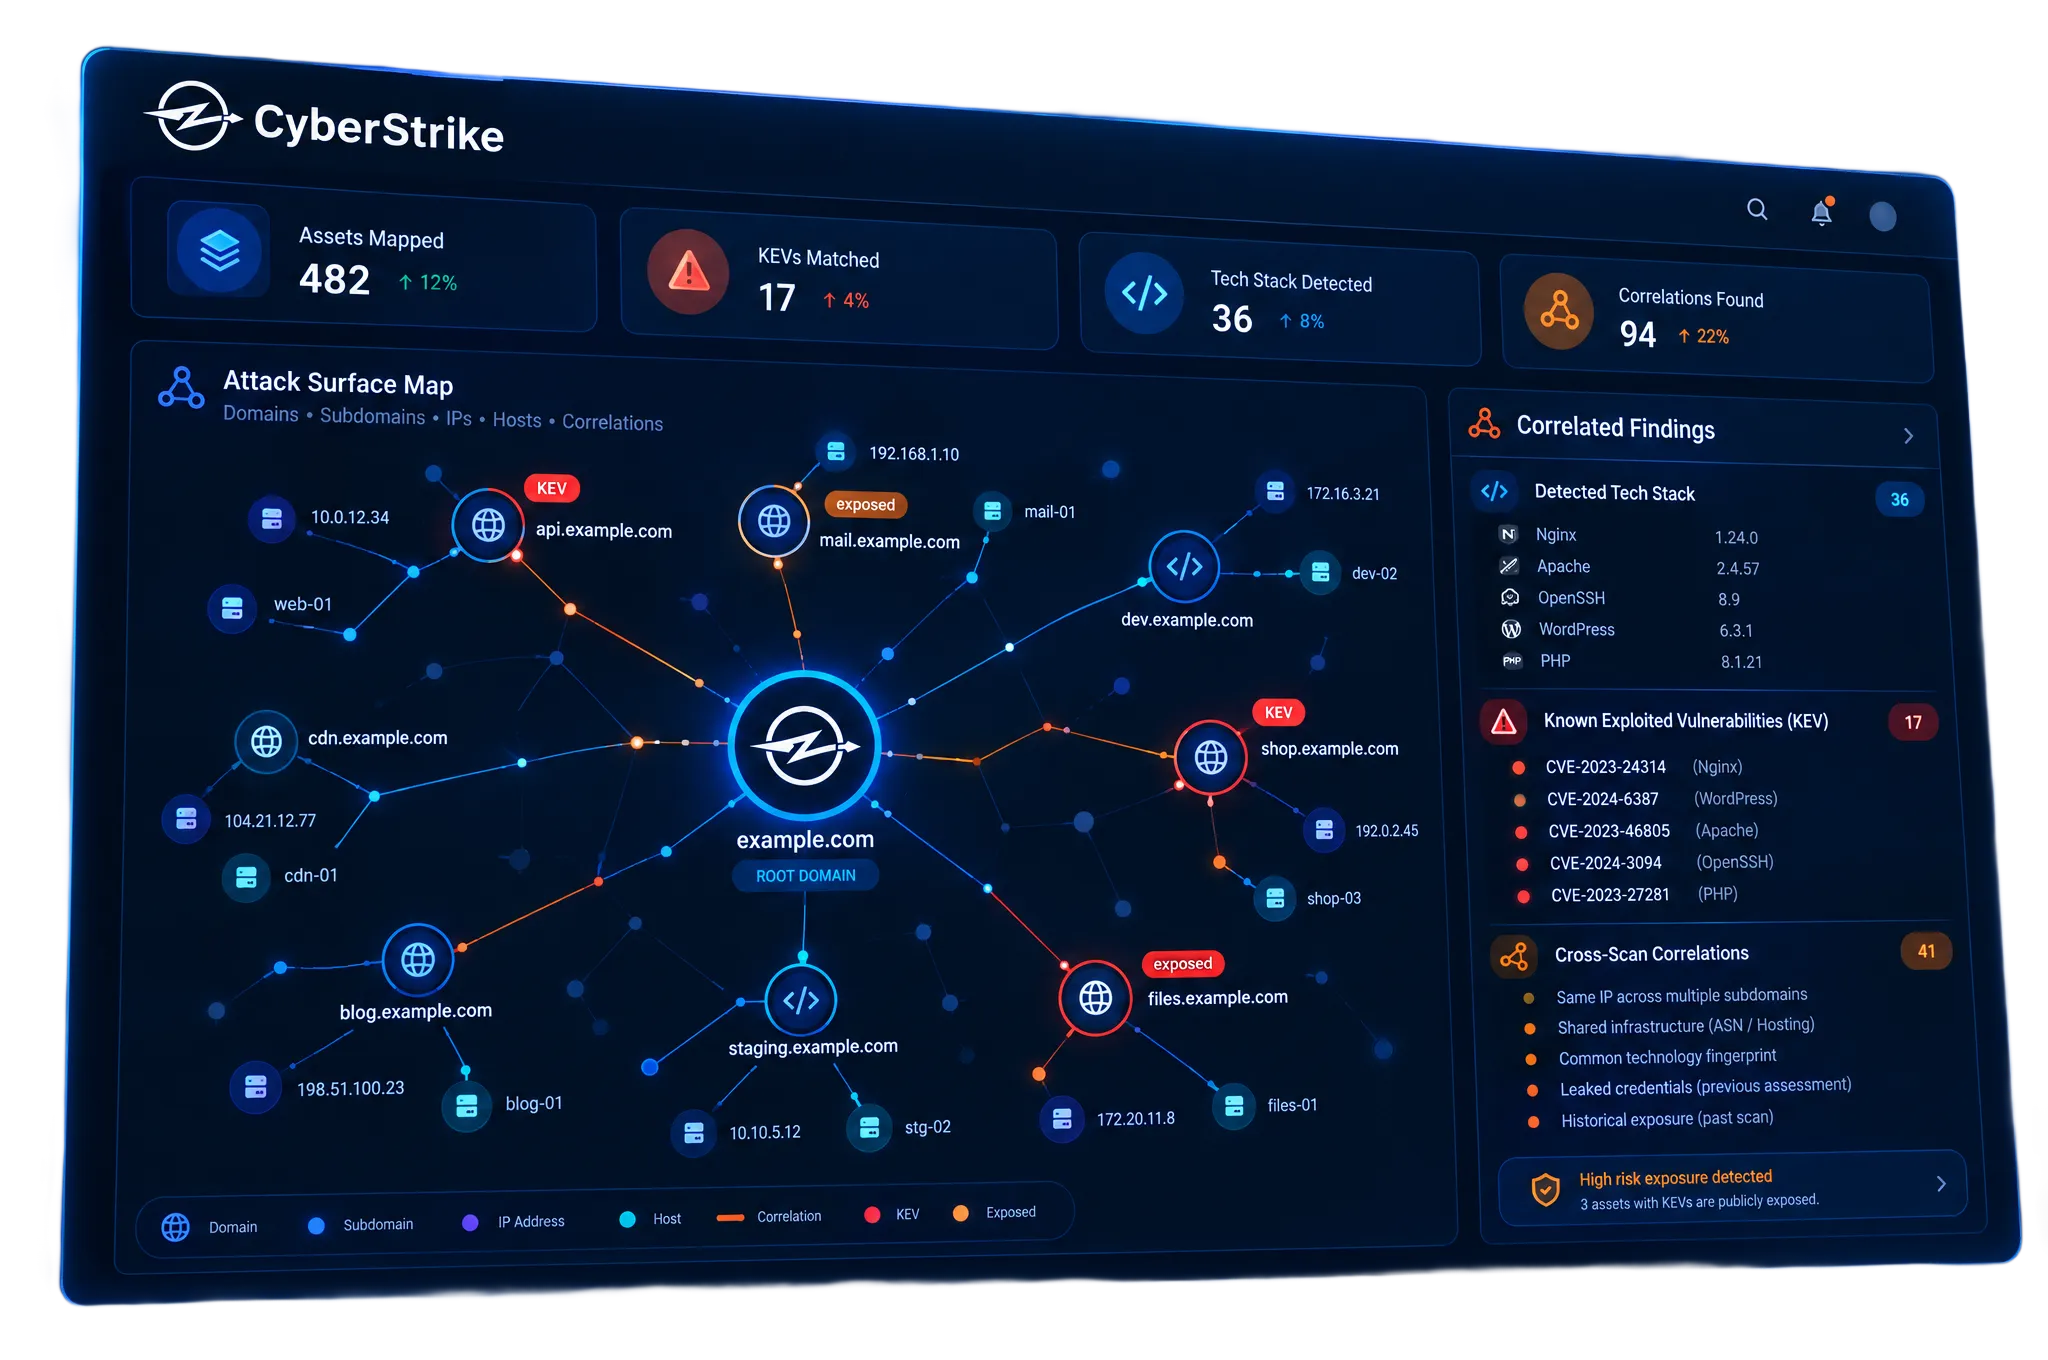
Depth review across your whole history
CyberStrike's agents review the findings from your past tests and scans and correlate them across assets, pulling the threads that matter: known exploited vulnerabilities (KEVs) matched to your stack, the technologies and versions you run, shared infrastructure, and credentials leaked in earlier assessments.
Compliance
Human-led trust, machine speed
Every engagement ends in an audit-ready report, signed by a certified pentester, and built to meet the frameworks your auditors hold you to.






