
Red-team the AI you're shipping
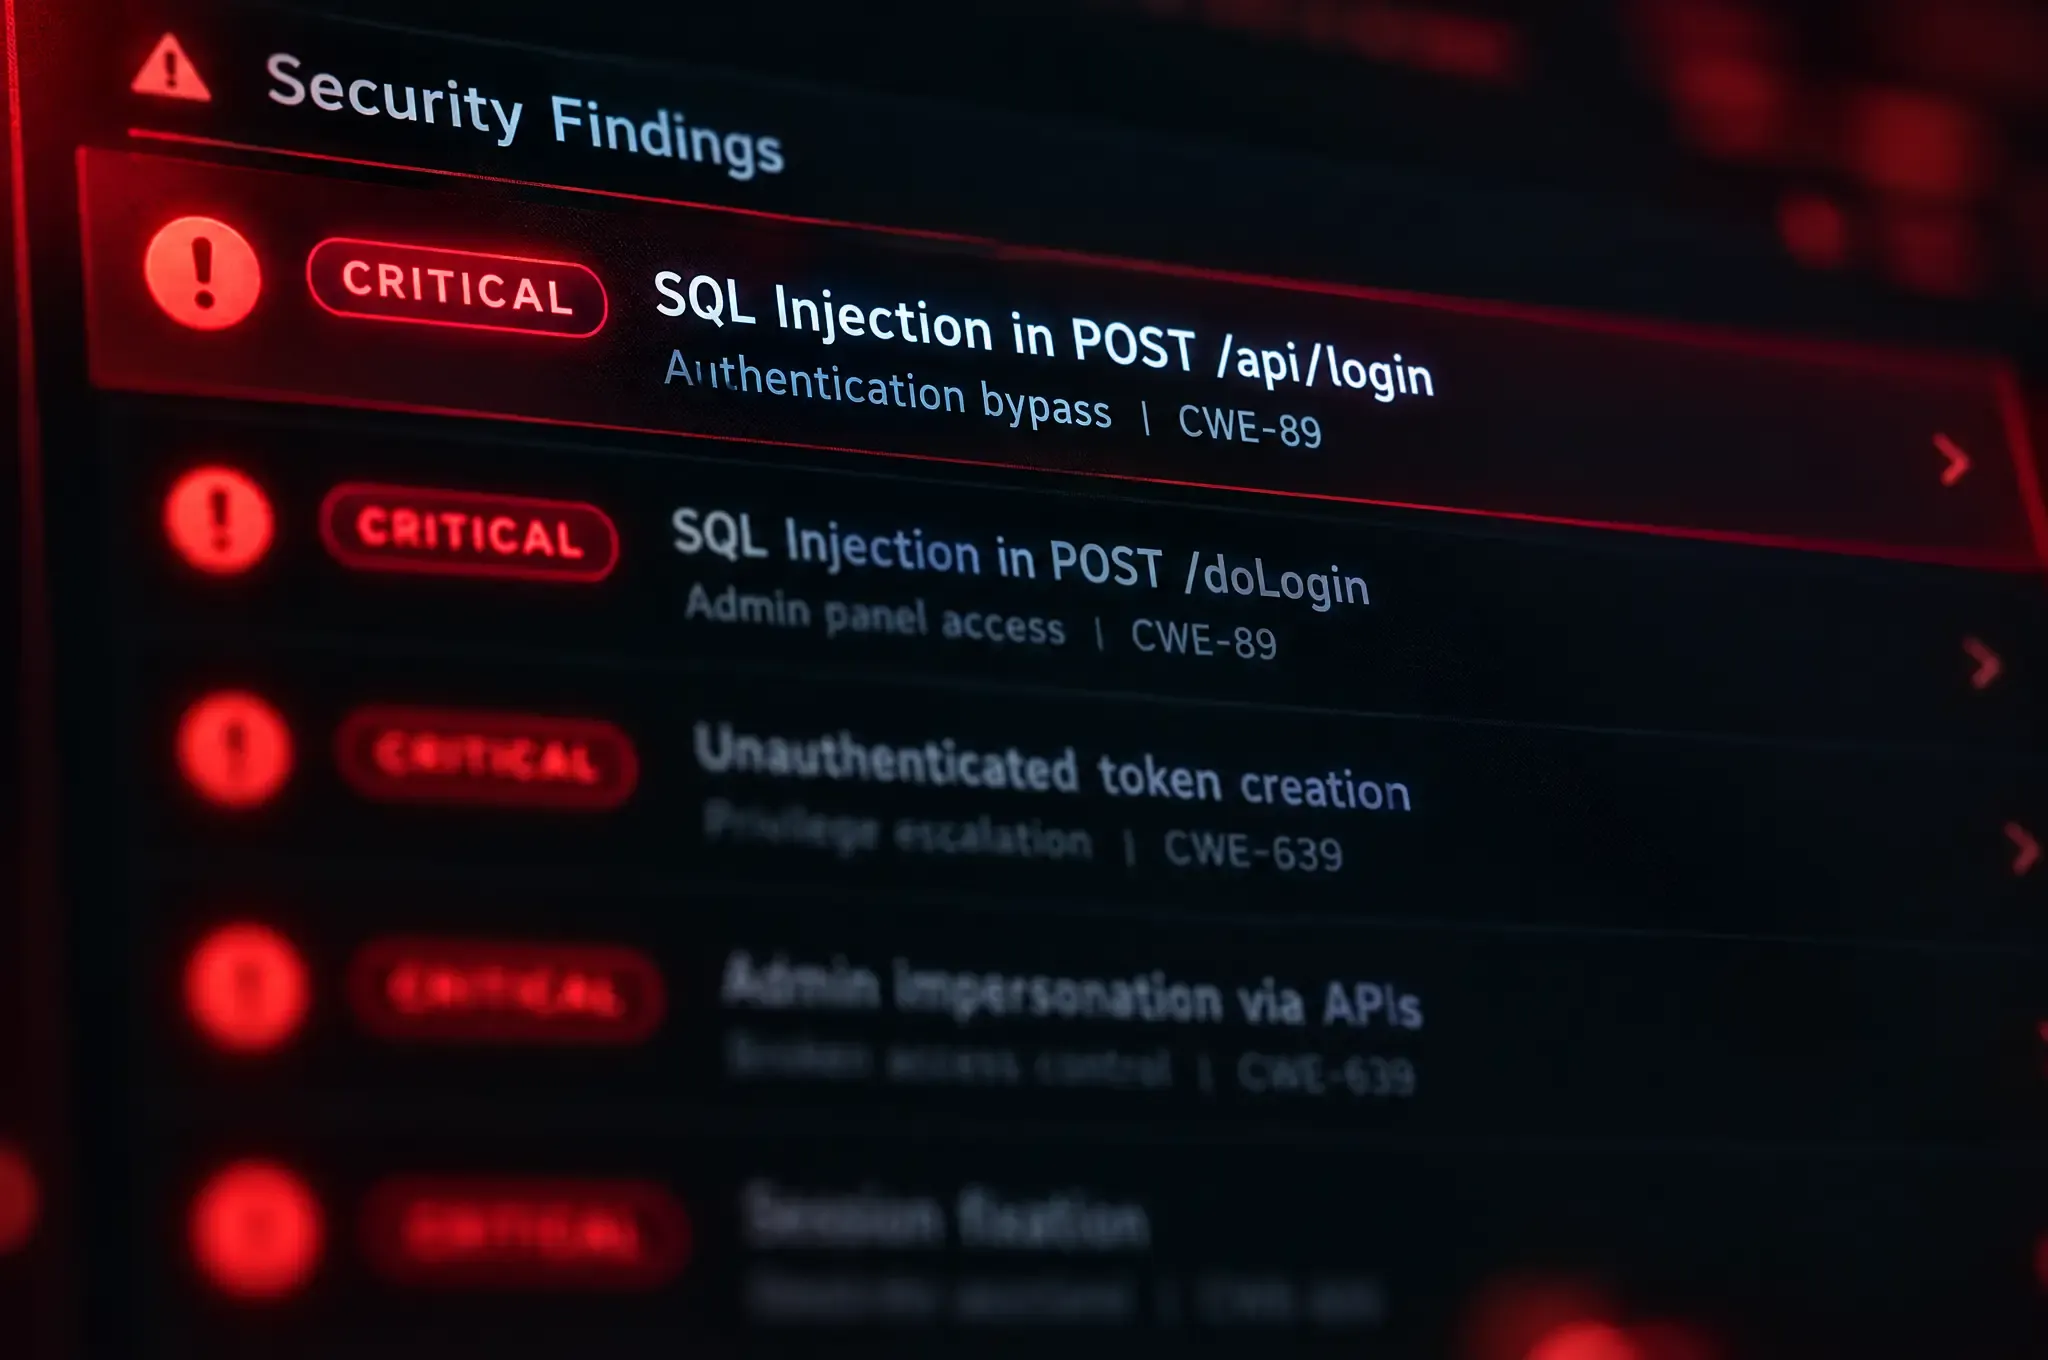
CyberStrike attacks your LLM apps, copilots, autonomous agents and MCP servers the way a real adversary would, surfacing prompt injection, data leakage and tool abuse, and proving each one exploitable before it reaches production.
The hardest targets, solved together
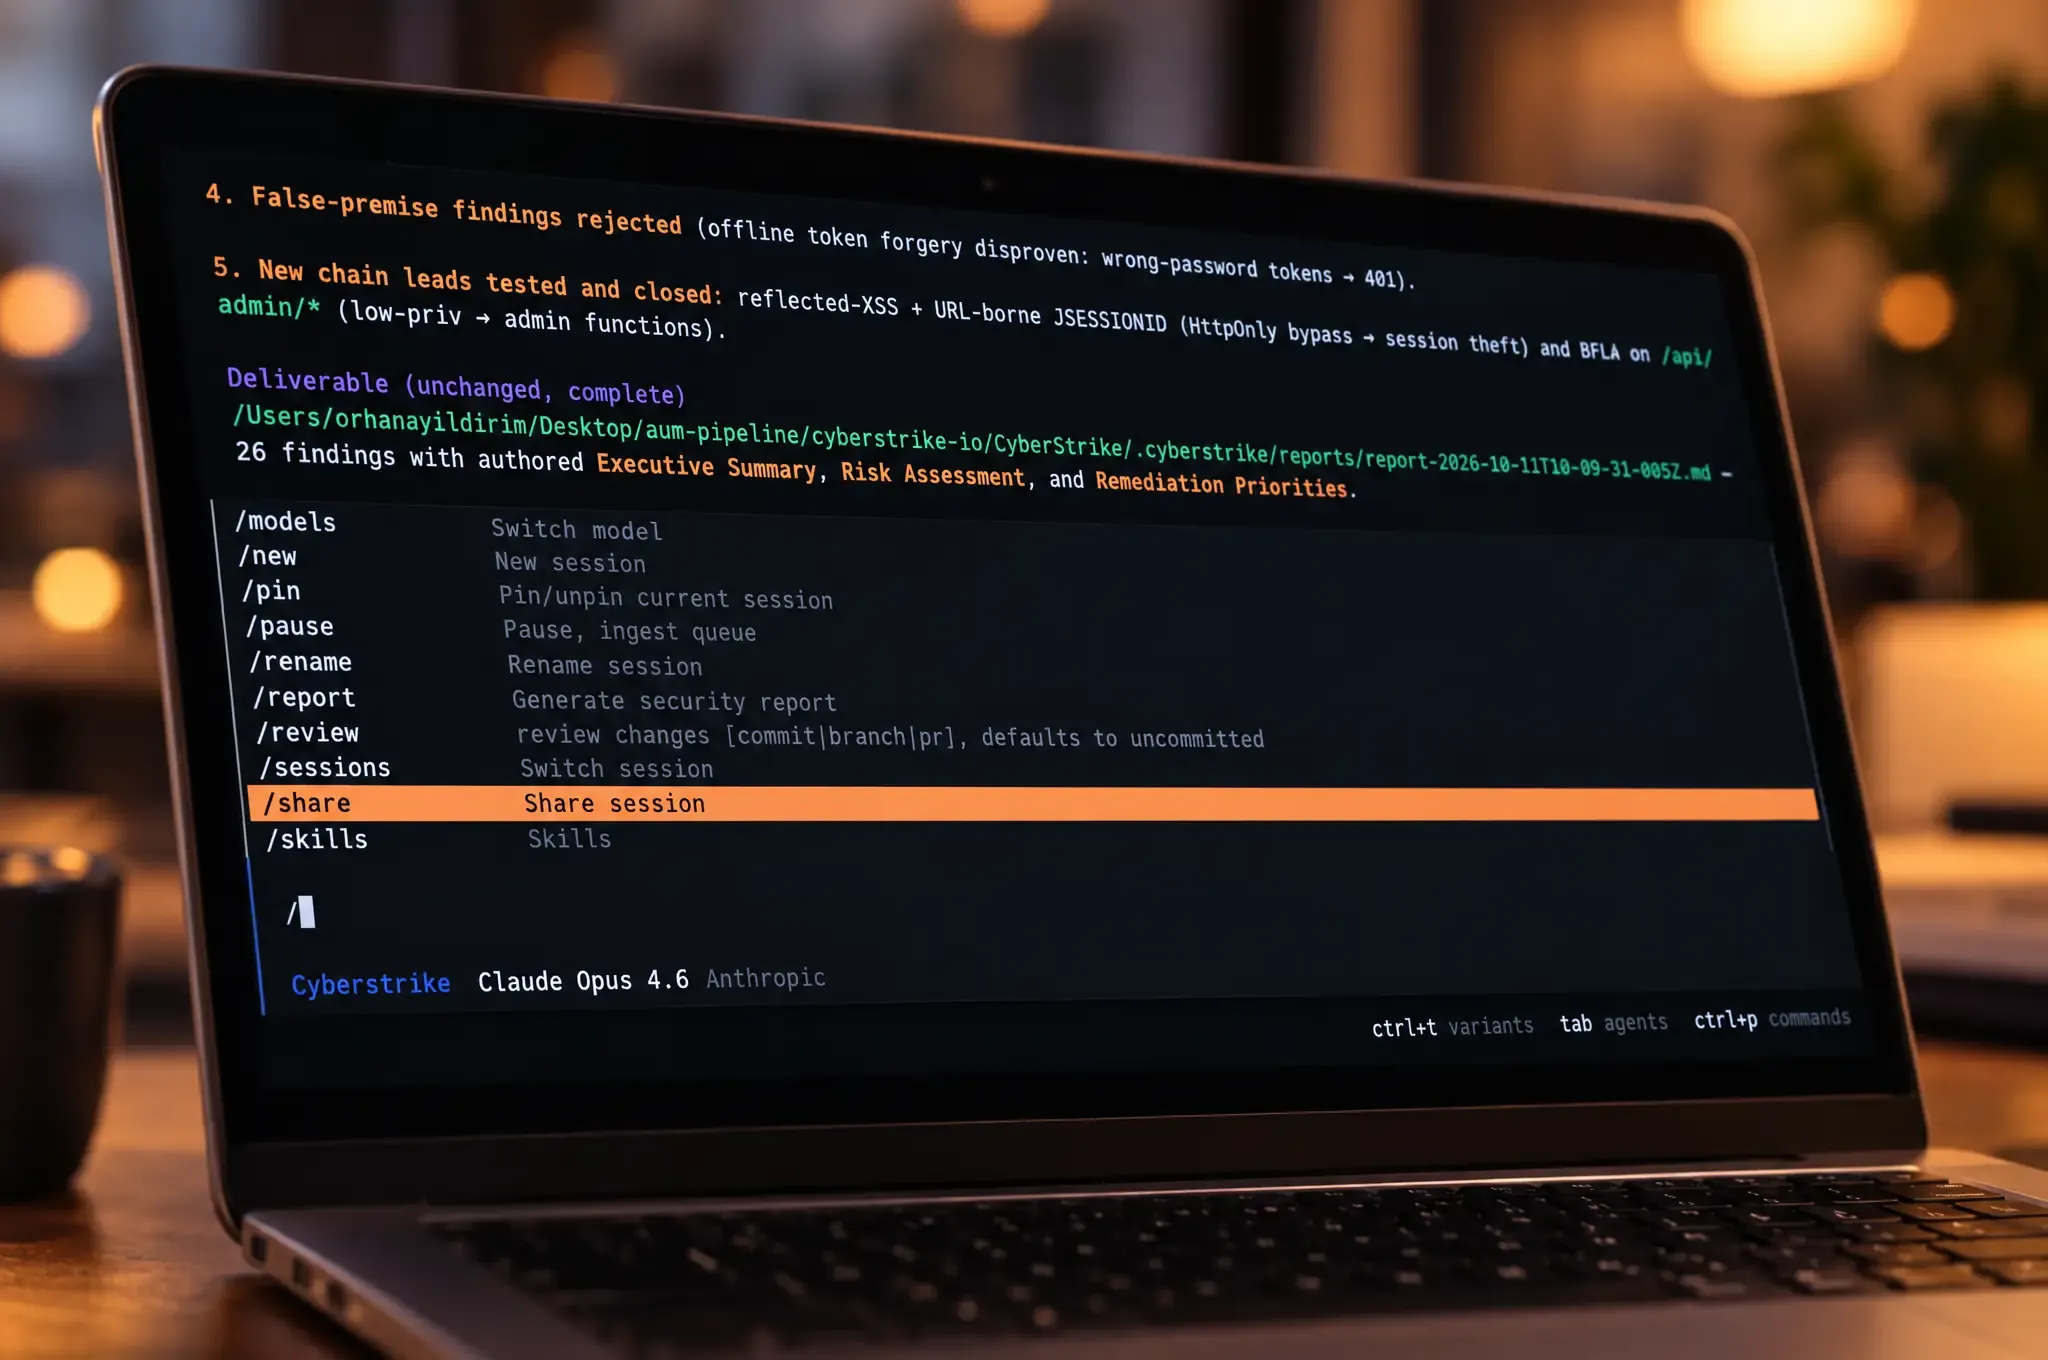
Share a live session with your experts
Some engagements need people and agents side by side. Share a running CyberStrike session so several human experts and the full agent team drive the same test together, in real time, with no handoffs and no lost context, until the hardest target gives.
Bolt runs your tools where the targets live
Bolt is a containerized MCP server that packages your security tools and runs them wherever you need: a VPC, an internal segment, or an isolated lab. Each tool is exposed directly, with no meta-tools and no dynamic loading, so you call the one you need and nothing else.
Compliance
Human-led trust, machine speed
Every engagement ends in an audit-ready report, signed by a certified pentester, and built to meet the frameworks your auditors hold you to.






