
Assume the breach, map the blast radius
CyberStrike works from an internal foothold the way an intruder would: enumerating Active Directory, surfacing exposed services and databases, and tracing how far one compromised host can move across your network.
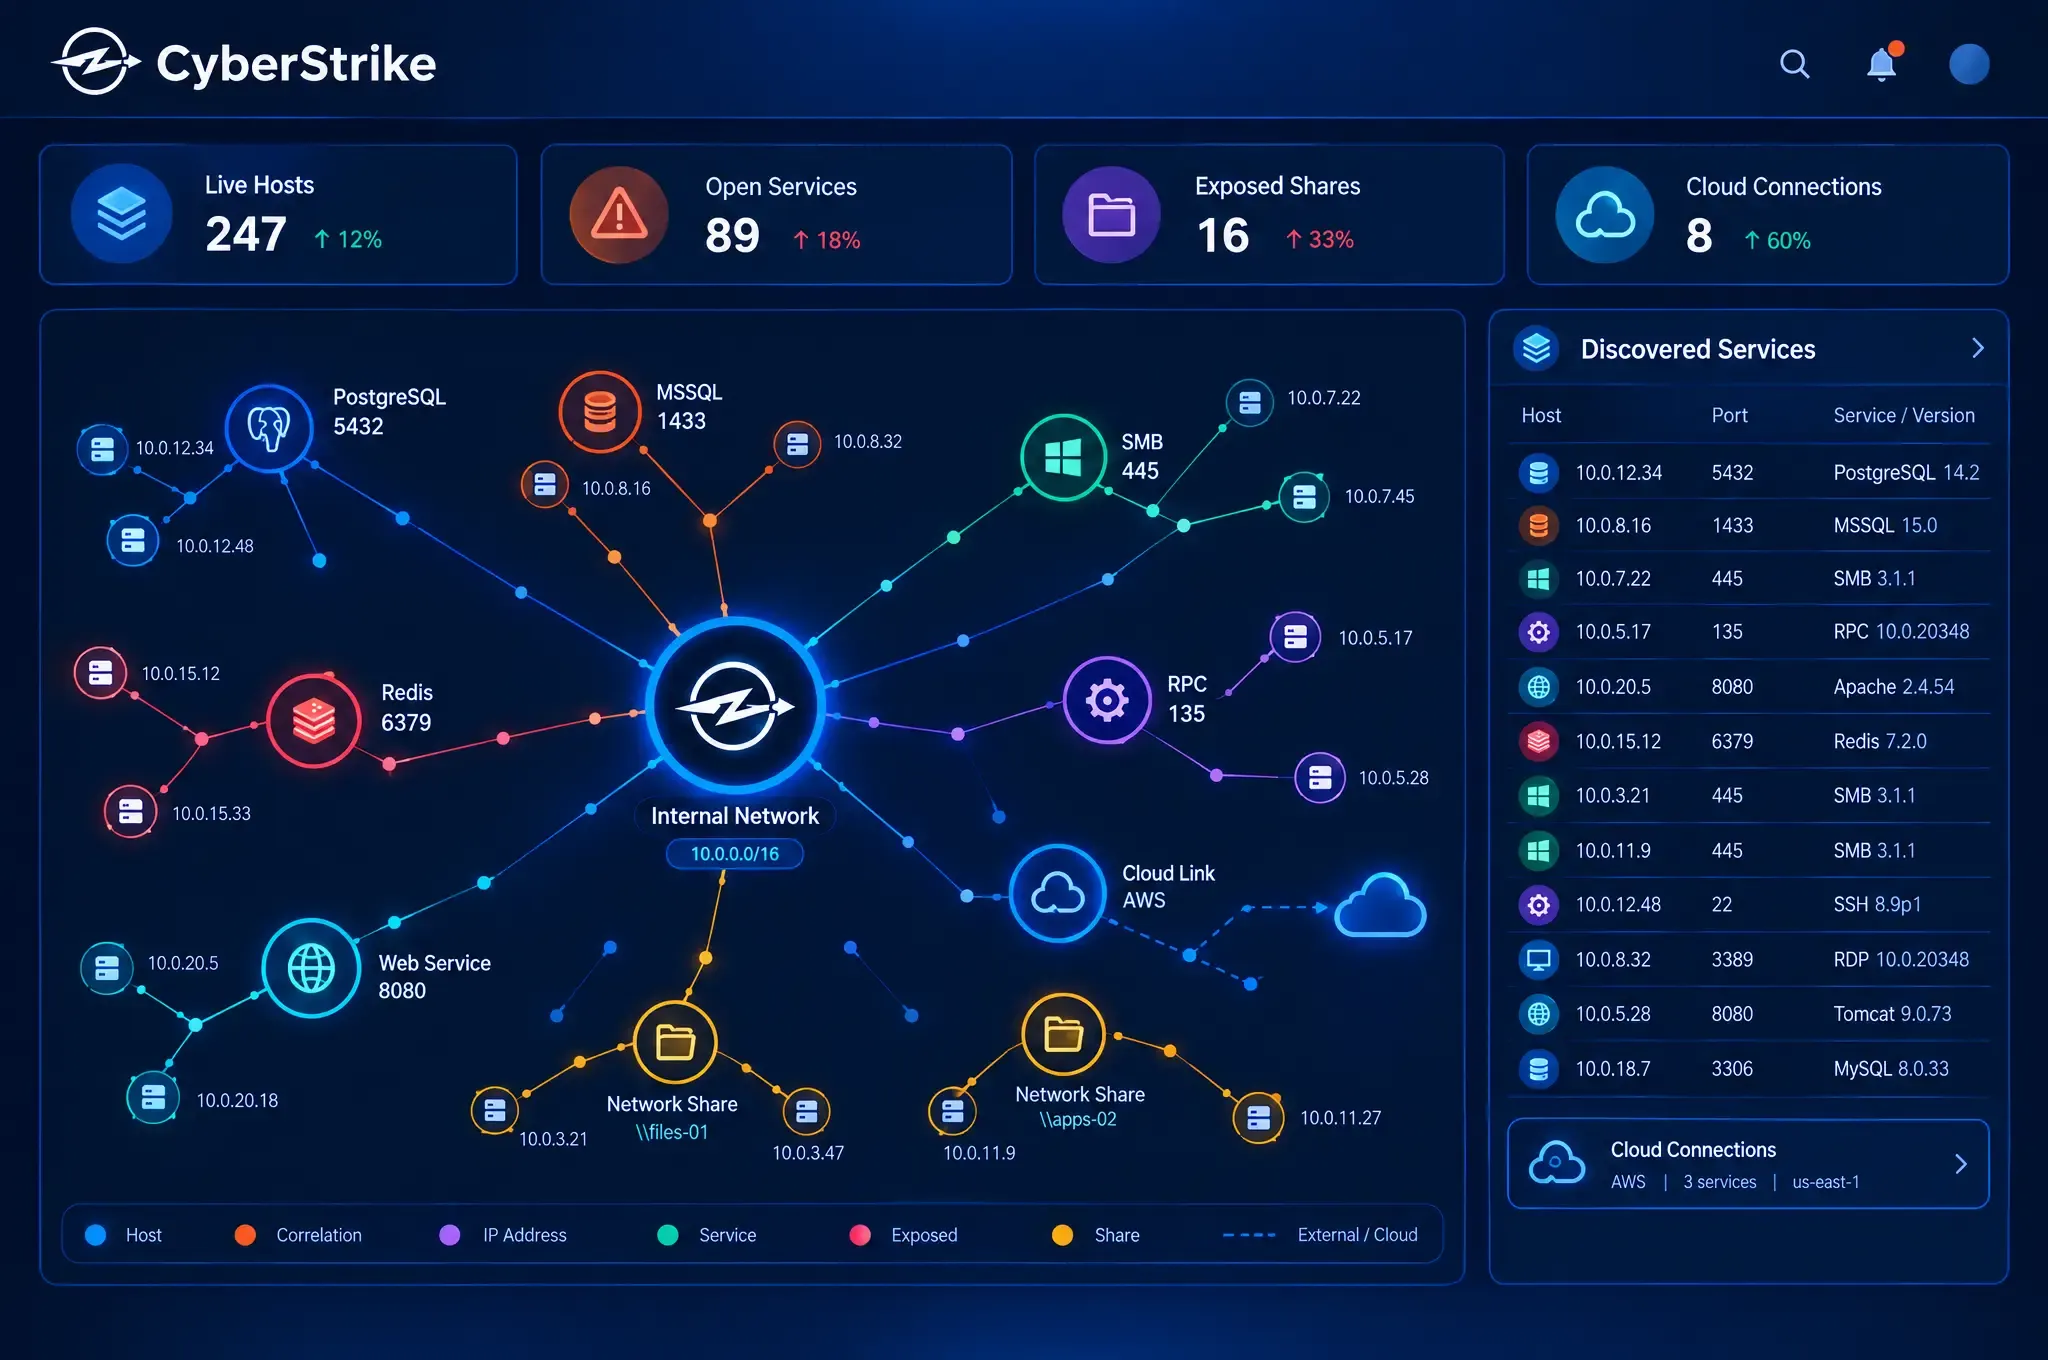
From a flat domain to a mapped attack graph
Every path to Domain Admin, surfaced
CyberStrike enumerates users, groups, ACLs and Kerberos tickets, then chains the misconfigurations an attacker would: Kerberoastable service accounts, excessive GenericAll rights and forgotten privileges. The result is the shortest path from any foothold to Domain Admin, ranked by the risk of each step.
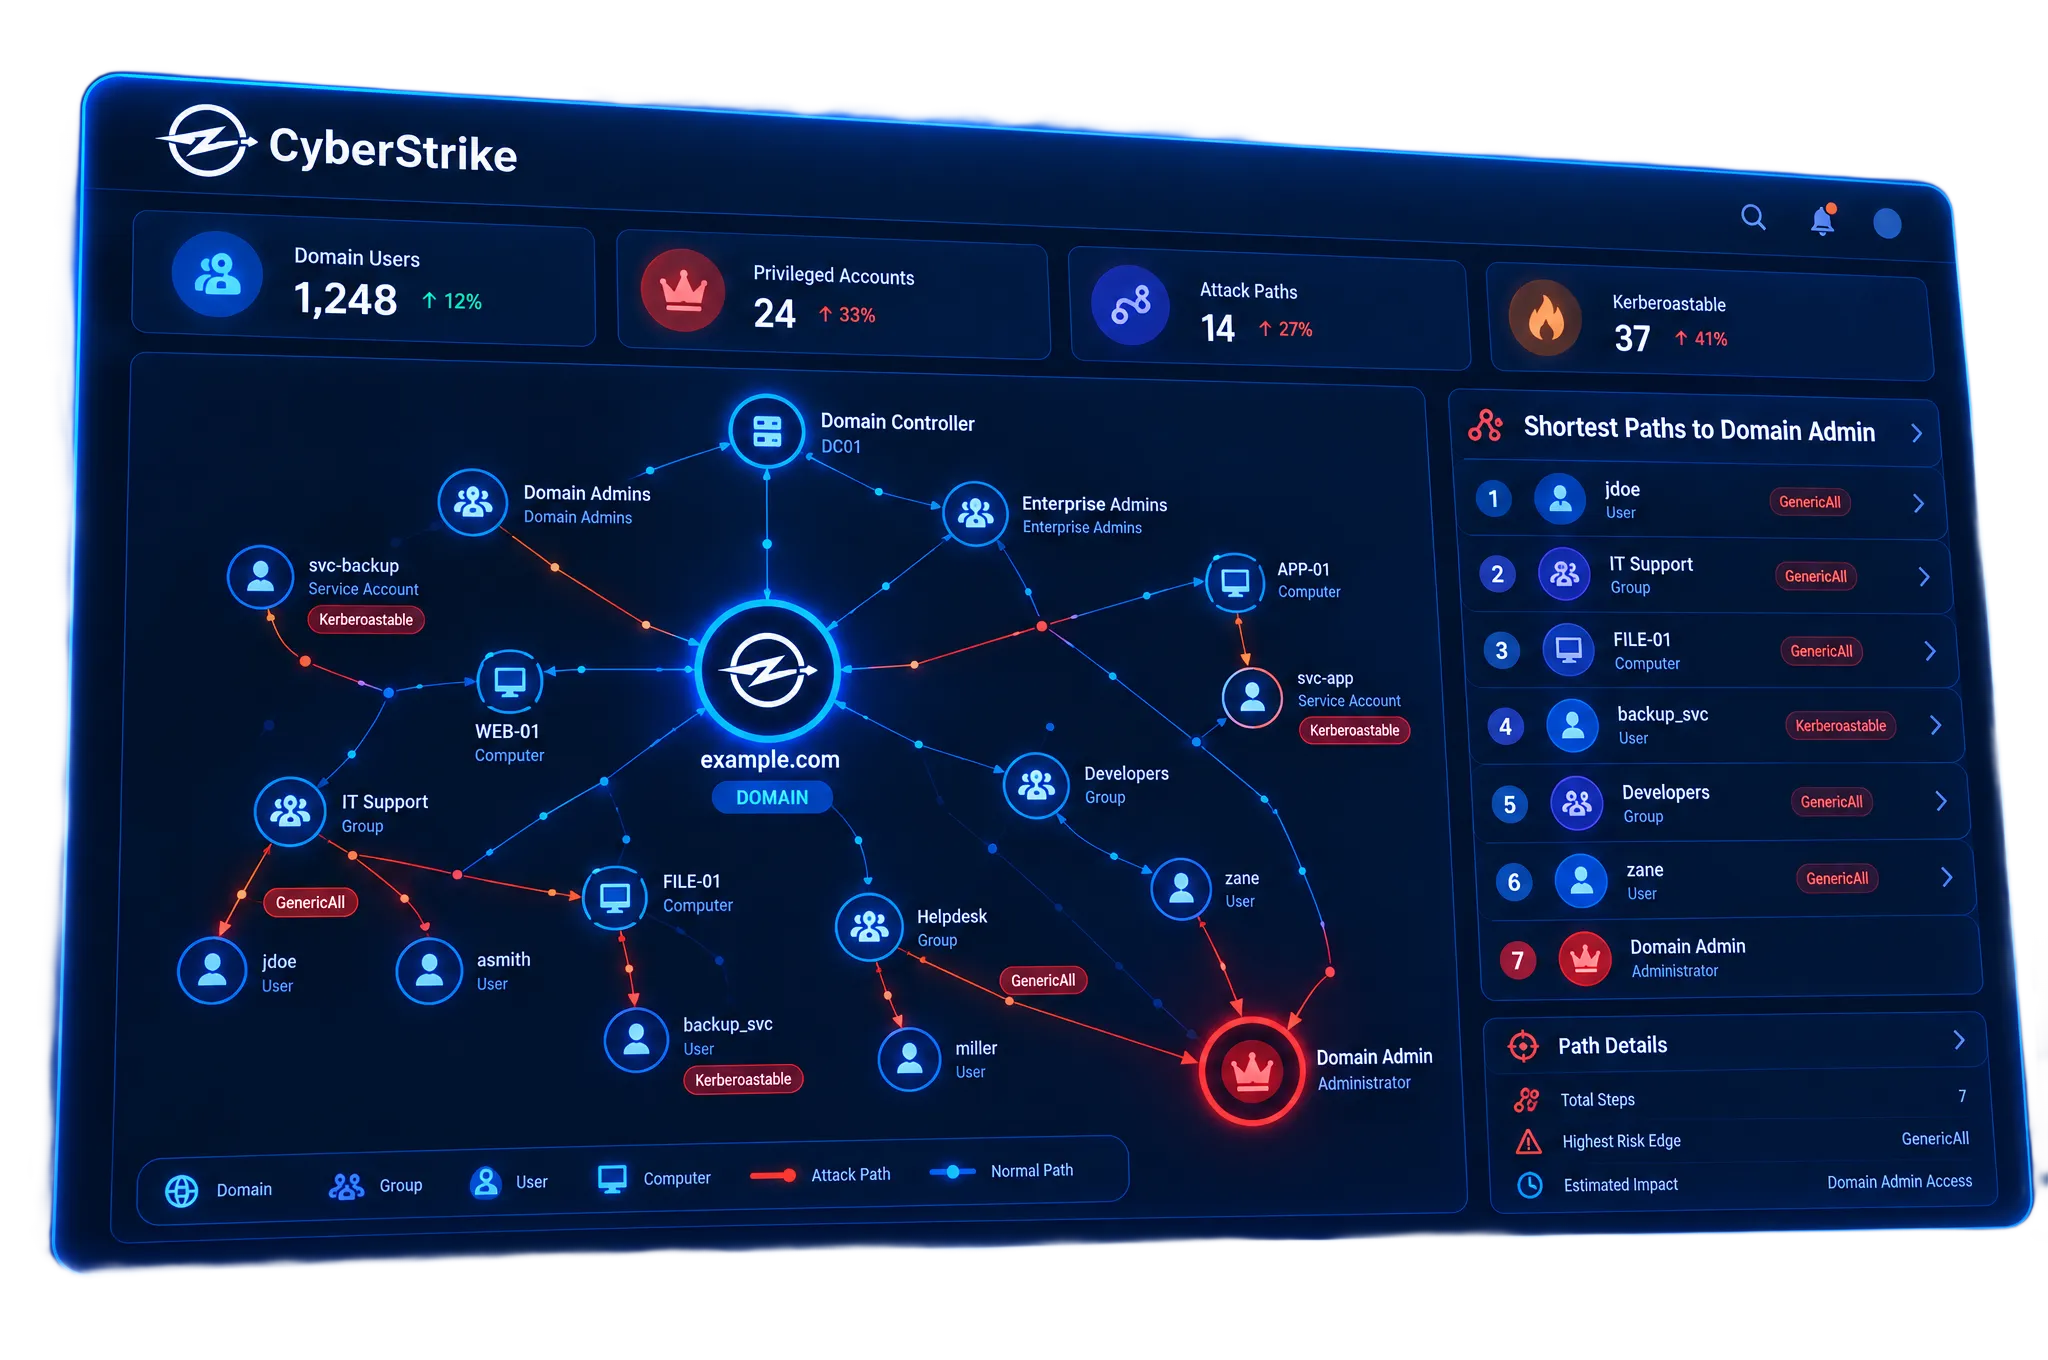
Inside the perimeter
What one foothold turns into
Active Directory
How a flat domain became a mapped attack graph
Read the storyInternal Services
How an exposed Redis cache was caught before it leaked
Read the storySegmentation
How open SMB shares were traced across 12 subnets
Read the story
Compliance
Human-led trust, machine speed
Every engagement ends in an audit-ready report, signed by a certified pentester, and built to meet the frameworks your auditors hold you to.






