
Go past the login, into the business logic
CyberStrike drives real browser sessions through your authentication and application flows, runs the full OWASP WSTG methodology, and proves every finding exploitable, so your team acts on real risk in web and internal apps, not scanner noise.
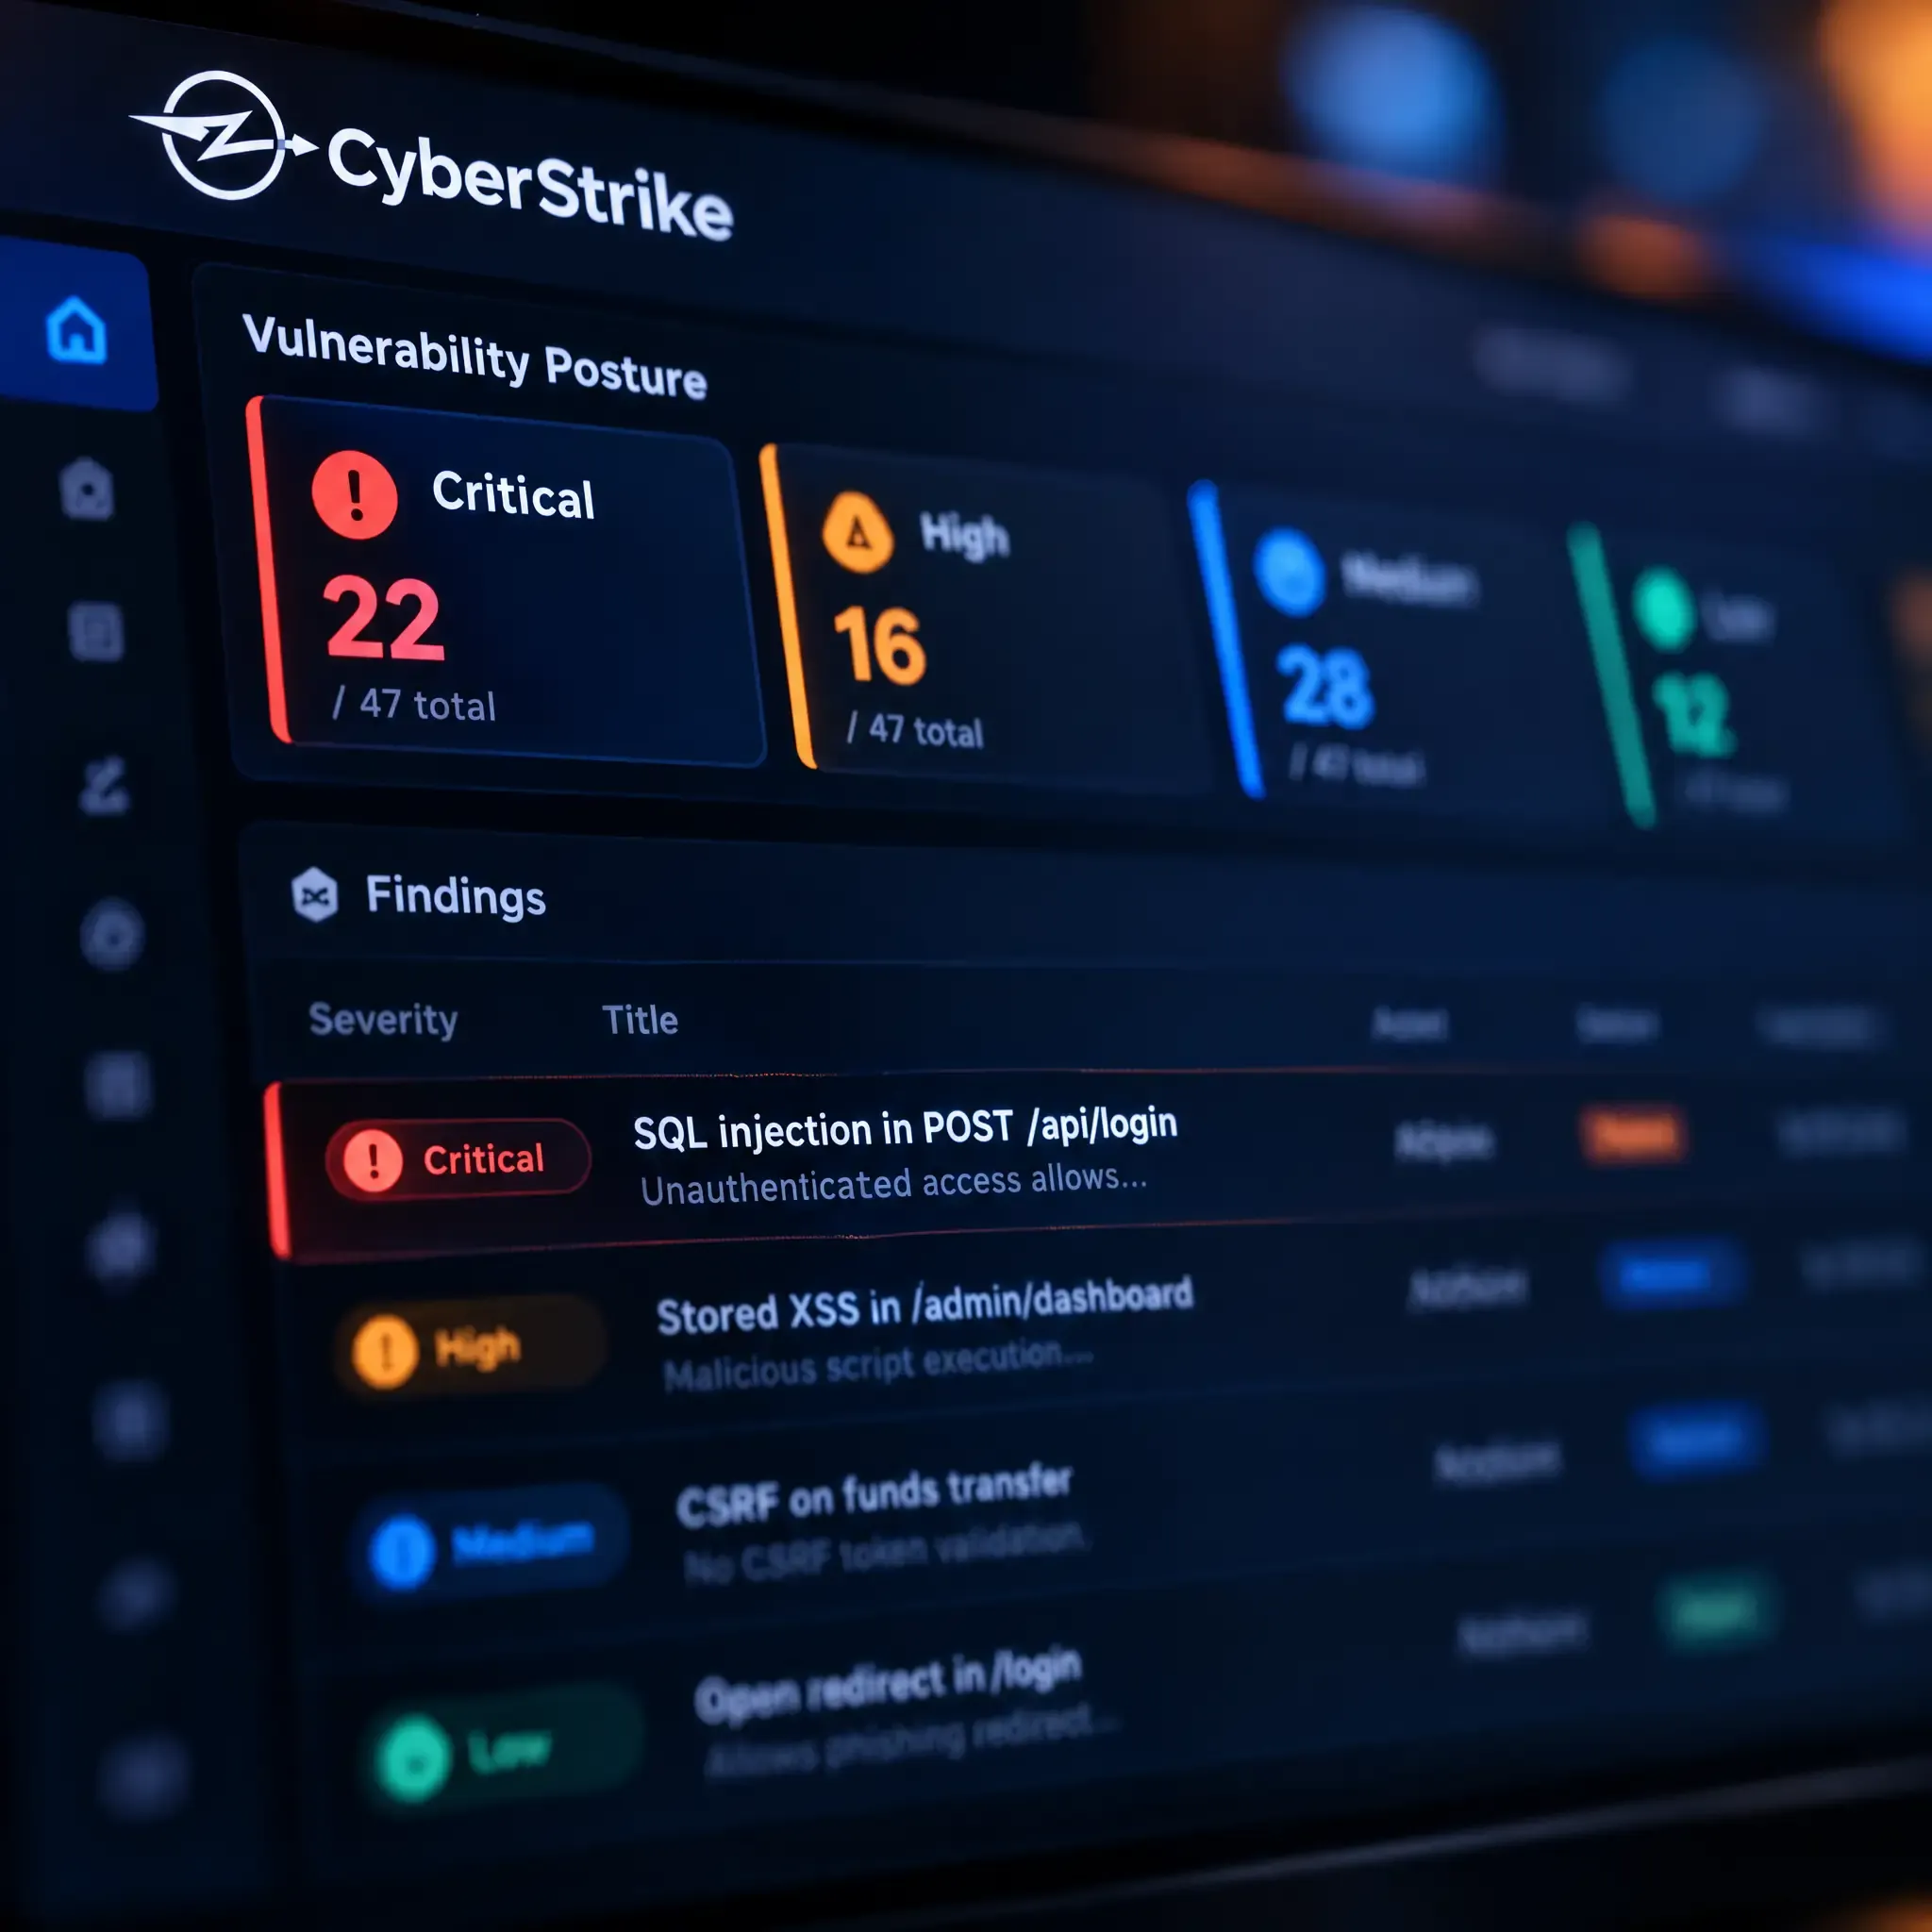
One platform. Every attack chain that matters.
From one weak endpoint to account takeover
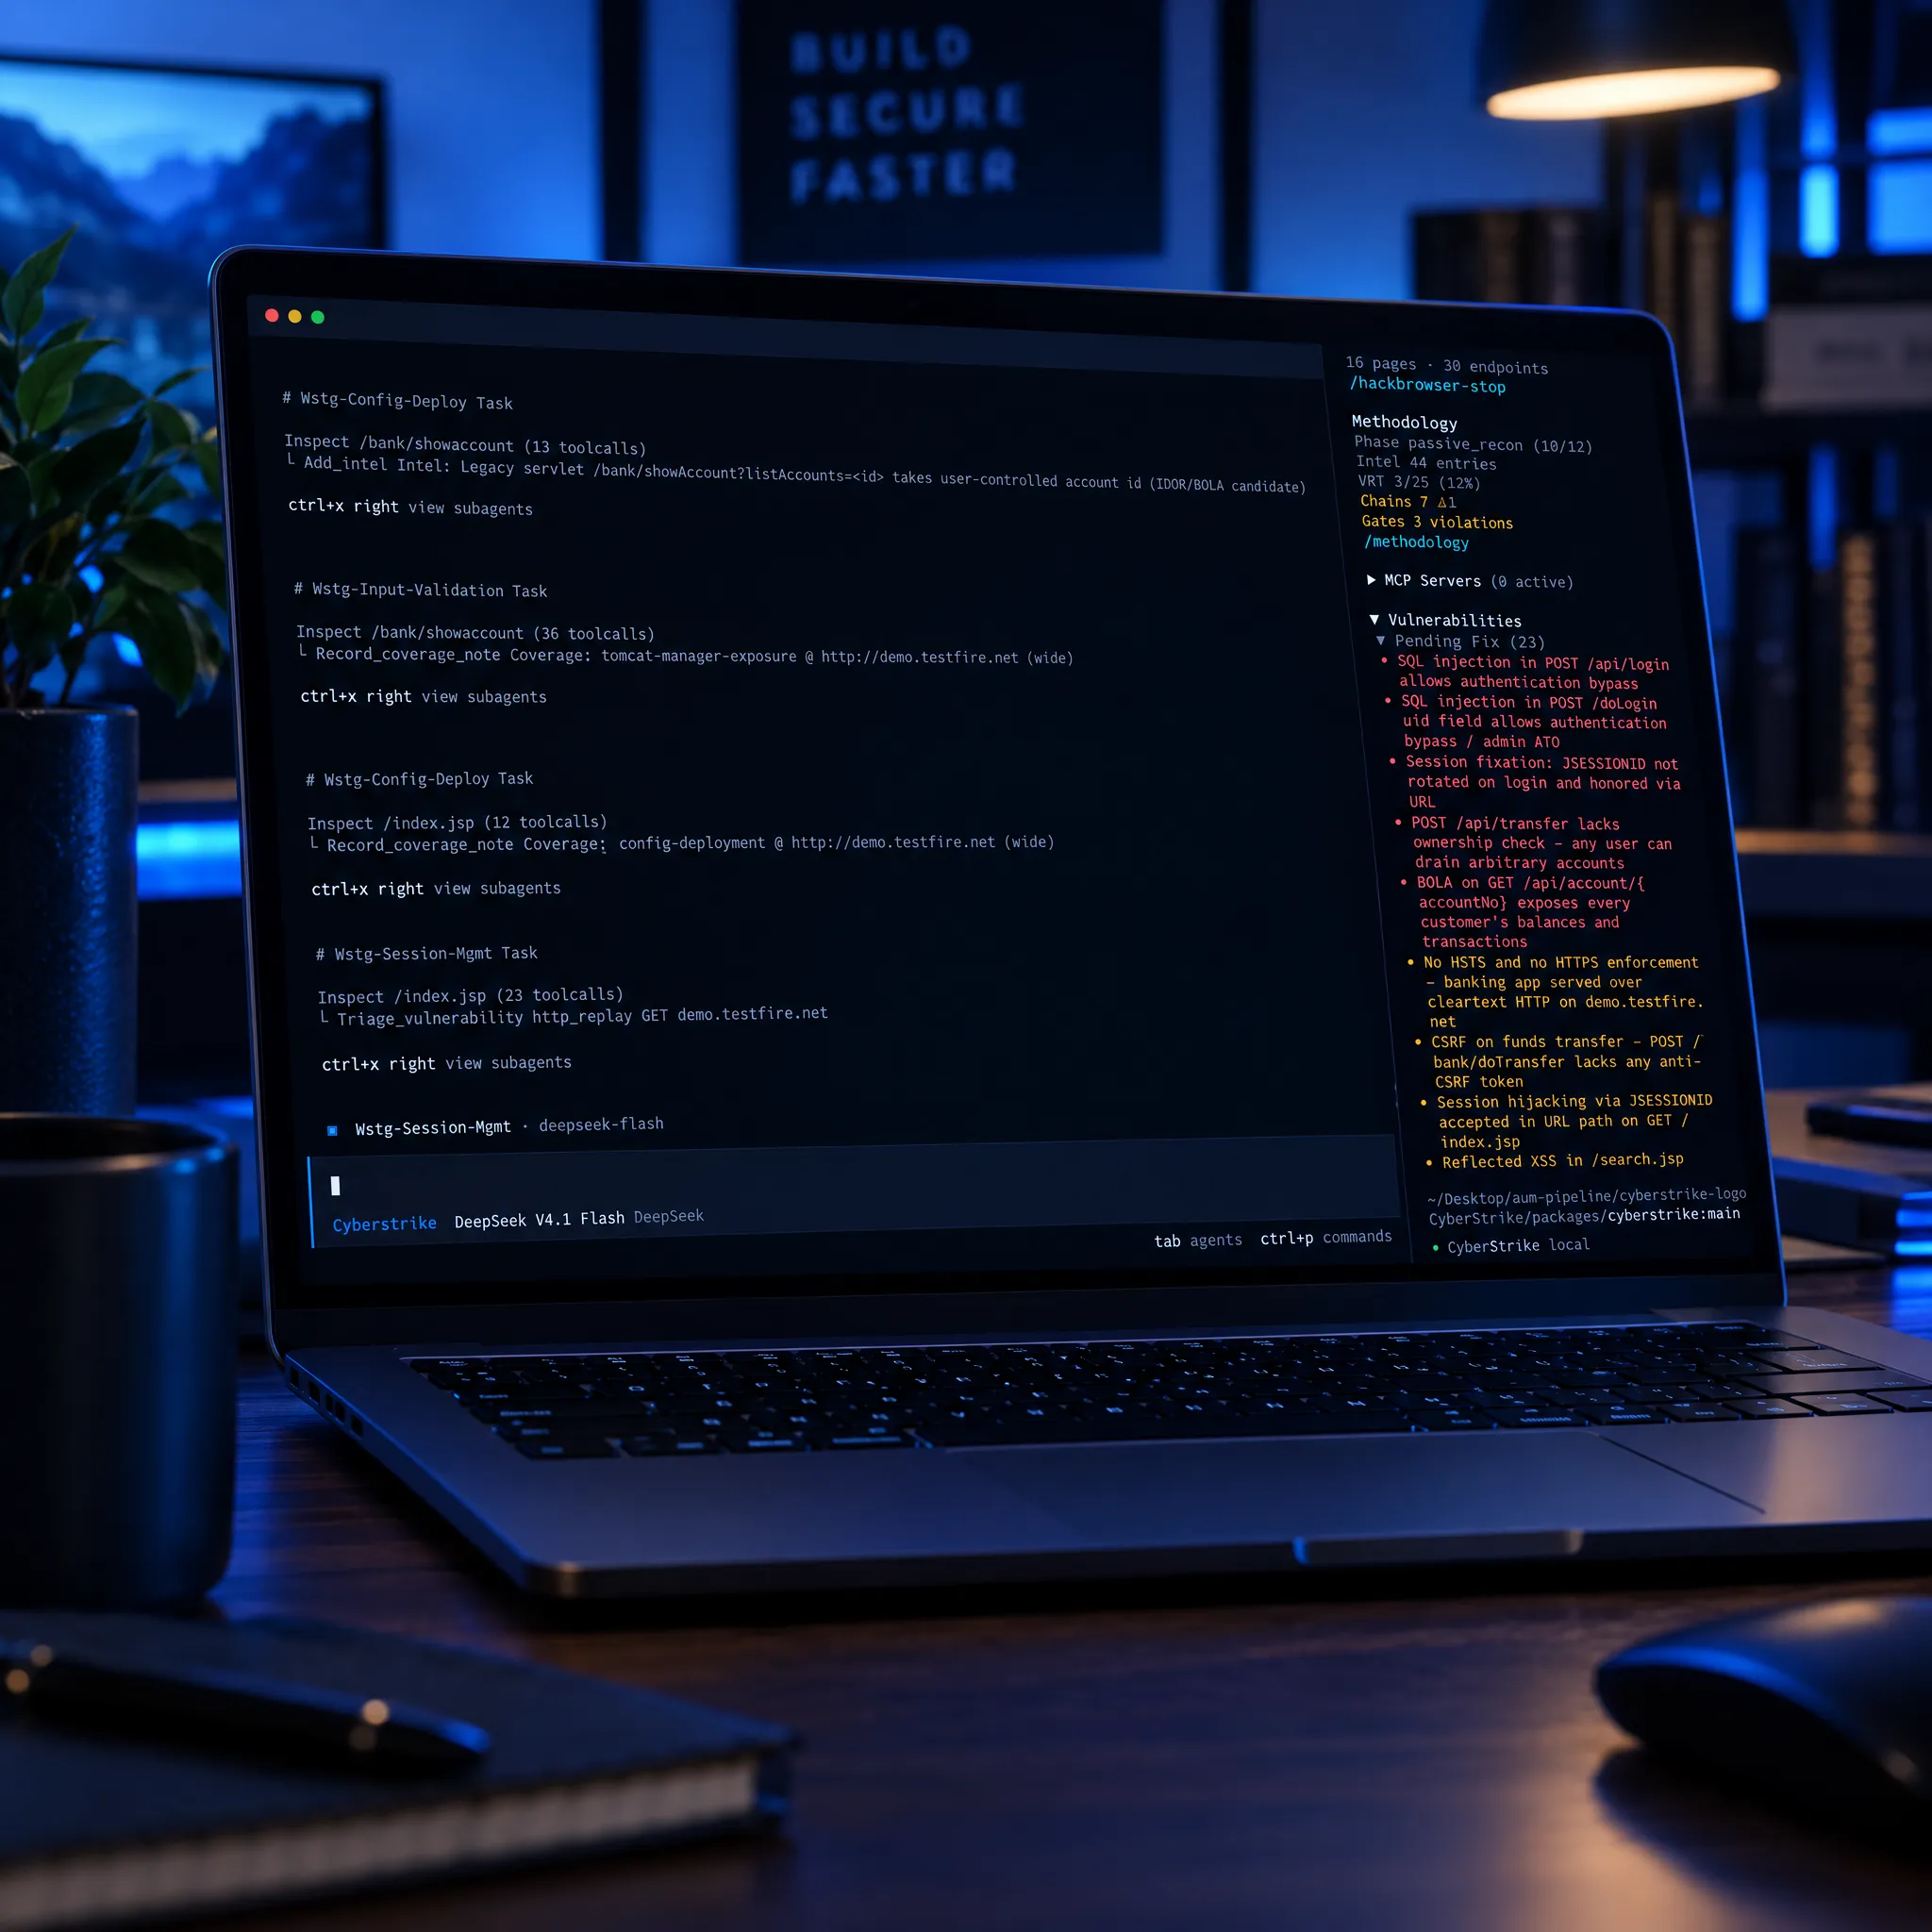
CyberStrike doesn't stop at isolated findings. Its agents chain weaknesses the way a real attacker would, escalating from an exposed endpoint to a full account takeover, and prove every step with a working proof of concept.
How a CyberStrike run works
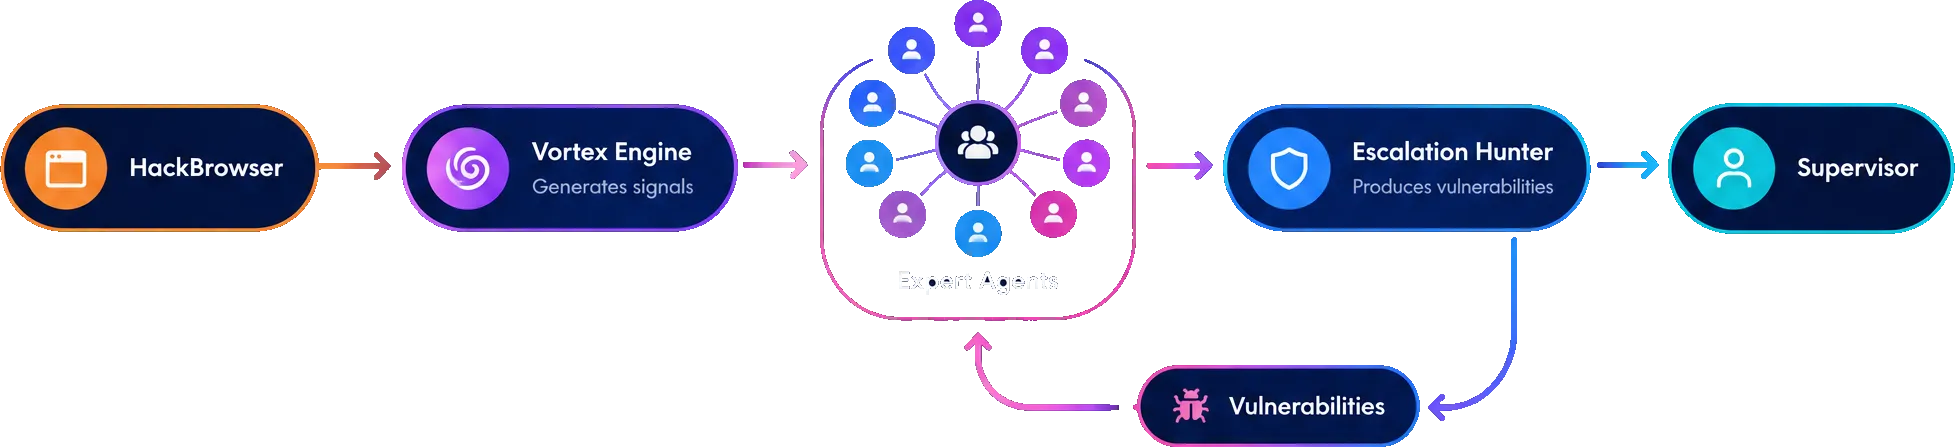
Hack Browser drives and maps the target, the Vortex engine turns raw traffic into signal, and a team of expert agents runs the full OWASP WSTG methodology. An escalation hunter chains their findings into real, exploitable vulnerabilities, looping back for deeper testing until a human supervisor signs off.
Compliance
Human-led trust, machine speed
Every engagement ends in an audit-ready report, signed by a certified pentester, and built to meet the frameworks your auditors hold you to.






